Open the original source
The exact page or record stays attached so the reviewer can distinguish live evidence from copied or stale information.
Ask what a public company surface can reveal, then see how Hide turns observed signals into owned, bounded work.
General information from an AI assistant, not a real check. Private by design, never sold or used for training.
Hide separates what a source actually shows from what it might mean, so public company exposure becomes a bounded review rather than an alarming dashboard.
Ownership, mail policies, certificates and public DNS records are shown with their source and observation time.
Indexed files, job listings and public pages are reviewed for operational detail that was intentionally or accidentally disclosed.
Related domains, public roles and company names stay separate until there is evidence connecting them.
A signal that cannot be verified remains unknown instead of being turned into a pass, breach or synthetic risk score.
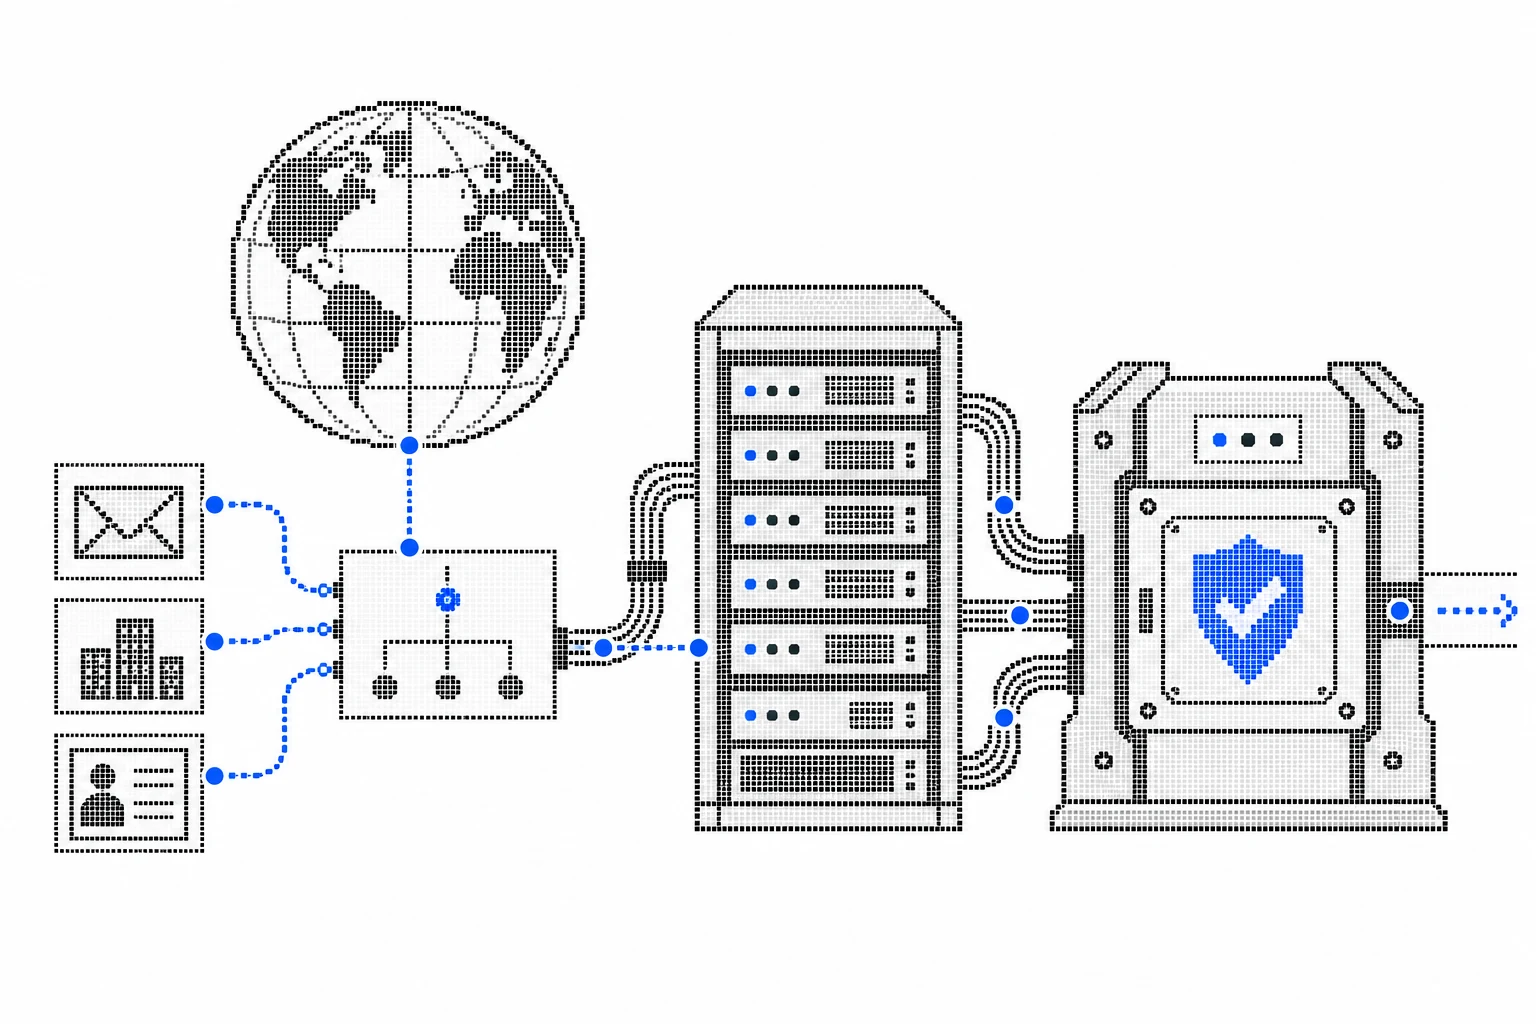
The exact page or record stays attached so the reviewer can distinguish live evidence from copied or stale information.
A domain, document or process finding goes to the team that can confirm context and approve the next step.
Corrections, accepted exposure and future monitoring remain in one private company record with dates and evidence.
Hide works from approved public sources. It does not probe private systems, attempt access or claim that a visible signal proves compromise.
Verify your company